Our Work · Plugins
Security Scanner for PHP: WordPress security in plain English
Built by Gorman Web, Security Scanner for PHP checks the whole PHP stack behind a WordPress site, from the PHP version and its settings to WordPress core, plugins and themes, then gives you a security score and a fix plan written in plain English. It is read-only, so it can’t break the site it is protecting.
What Security Scanner for PHP checks
One scan covers four areas of a WordPress site. The first two are free; the paid plans add the other two.
PHP version and settings
End-of-life and soon-to-expire PHP versions, missing PHP security patches such as the PHP2Shell fixes, and risky php.ini settings like allow_url_include, display_errors and public phpinfo() pages.
WordPress core, plugins and themes
Missing security releases, out-of-date and inactive plugins and themes, and plugins closed on WordPress.org, plus risky settings such as open registration with an admin-level role, public debug logs, default security keys and an “admin” username.
Malware and file integrity
Every PHP file checked for web-shell and backdoor signatures, PHP in uploads, malicious .htaccess and .user.ini rules, and exposed .git, .env, backup and database files, with core and plugin files compared to their official versions.
Composer libraries
Every bundled PHP library your plugins and themes bring along, checked against the OSV.dev vulnerability database.
The report
A security score and a fix plan anyone can follow
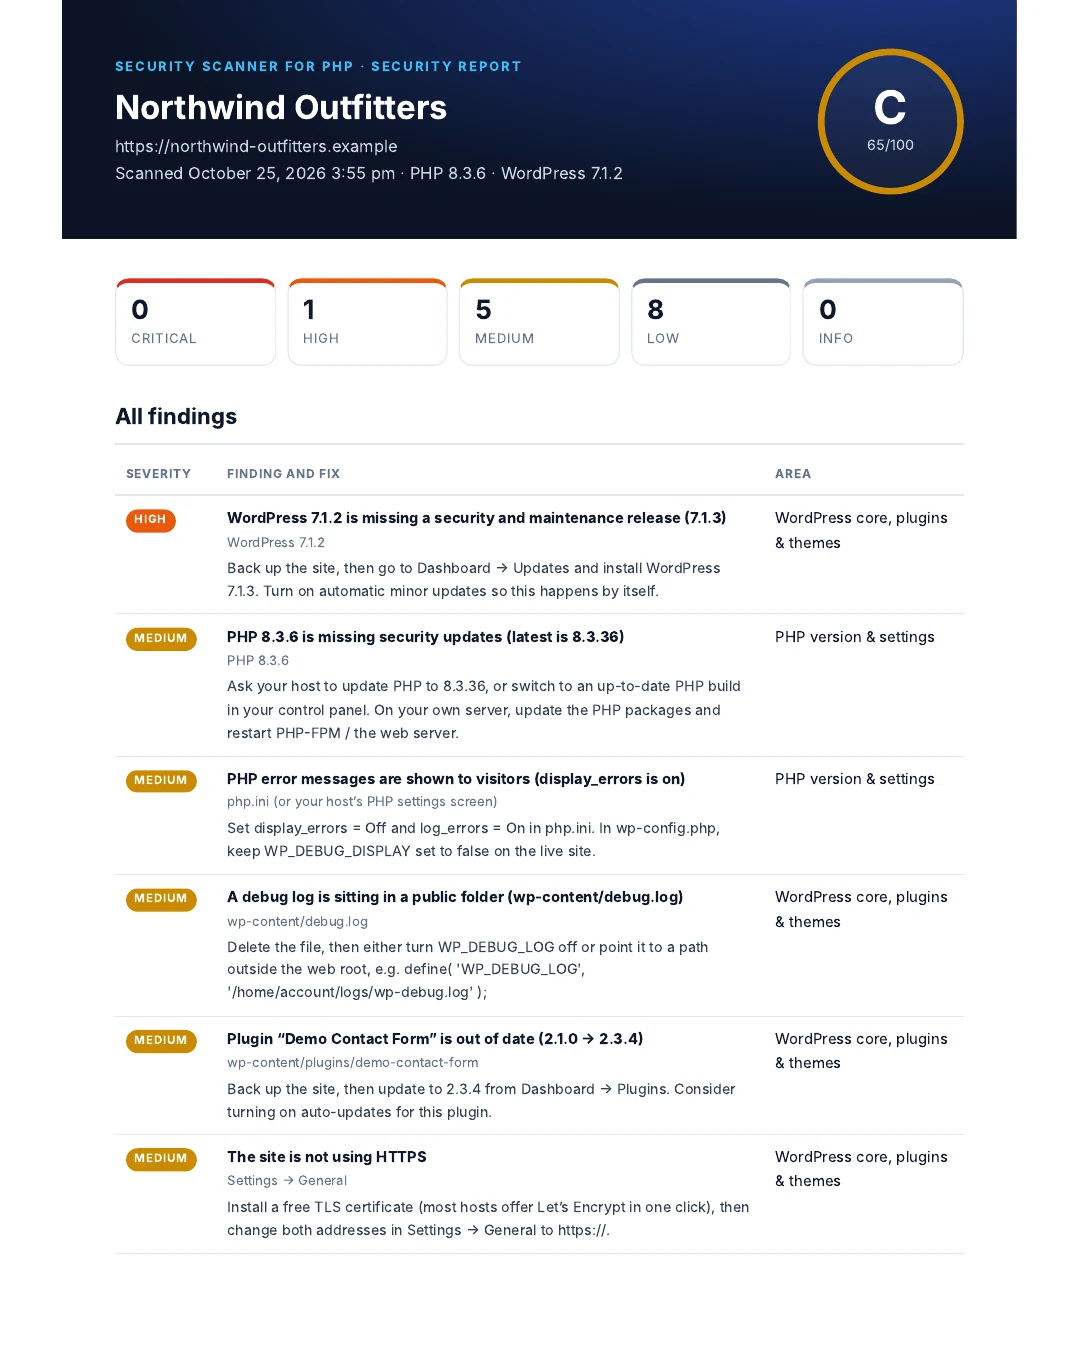
Every scan ends with a security score and a prioritized fix plan: a short summary for the site owner, a “fix first” list, and step-by-step fixes for the developer. Click any finding to see exactly what was found and how to fix it.
- A score out of 100 with a letter grade
- Findings sorted by severity, from critical to info
- The evidence behind every finding, so you can judge it yourself
- An ignore list for accepted risks, with the score updated to match
- Brandable client reports (print or PDF) in the paid plans
Read-only, so it can’t break your site
Security Scanner for PHP never edits, moves, quarantines or deletes a file. It reads files and settings, stores its own results in the WordPress options table, and leaves every fix to you or your developer.
It is a detection and guidance tool, not a firewall or a malware-cleanup service. If a scan finds a web shell, follow the fix plan or bring in a cleanup service.
Also included
- Latest PHP threats: PHP branch support status and the newest reviewed PHP advisories from the GitHub Advisory Database
- Shared hosting friendly: scans run in short, resumable slices
- Dashboard widget with your current score
- Requirements: WordPress 6.2 or later and PHP 7.4 or later
Plans and pricing
The free version includes the PHP and WordPress checks, the security score and the fix plan. Every paid plan starts with a 3-day free trial, no card needed.
Free
PHP version and settings, WordPress core, plugins and themes, the security score and the fix plan.
Pro
Everything in Free, plus every paid feature below for one site.
Studio
Every paid feature for up to five sites.
Agency
Every paid feature for up to 25 sites.
Every paid plan adds
- Malware and file-integrity scanning
- Composer library checks
- Scheduled scans (twice daily, daily or weekly) with email alerts for new critical or high issues
- Fix plans written by AI with your own Claude API key
- WPScan vulnerability lookups with your own token
- Brandable client reports (print or PDF), plus CSV and JSON exports
- White-label branding on reports and alerts
- A WP-CLI command for CI/CD pipelines and monitoring
Frequently asked questions
Is Security Scanner for PHP free?
Yes. The free version checks your PHP version and settings and WordPress core, plugins and themes, then gives you a score and a fix plan, with no license needed. The paid plans add the malware and file-integrity scan, the Composer library check, scheduled scans and client reports.
Will it change or delete files?
No. It only reads files and settings. It stores its own results in the WordPress options table and nothing else.
What data leaves my server?
Plugin slugs and versions go to WordPress.org, as WordPress itself already does. PHP version data comes from endoflife.date and advisories from GitHub. In the paid plans, Composer package names and versions also go to OSV.dev. No file contents are sent anywhere.
Does it replace a firewall or a malware-cleanup service?
No. It is a detection and guidance tool. If the malware scan in the paid plans finds a web shell, follow the fix plan or bring in a cleanup service.
What happens when a trial or license ends?
Nothing breaks. The free checks, the dashboard and the fix plan keep working. The paid scans, scheduled scans and alerts pause until a license is active again, and your settings and scan history are kept.
Can Gorman Web build a custom plugin for my business?
Yes. See Plugin Development or request a free quote.
Need a custom WordPress plugin?
Tell us about your business and what you need. You will get a straight answer and a free, fixed-price quote. Prefer to talk? Call 732-378-9766.